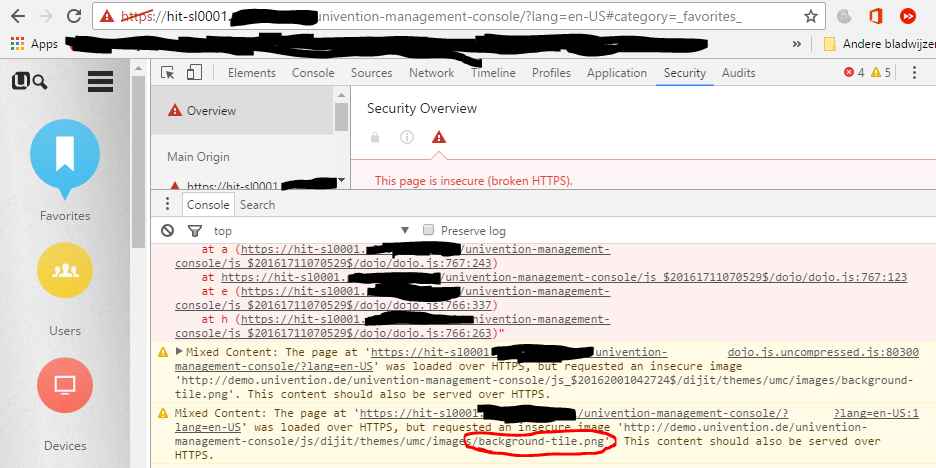
We noticed that our website for UMC (Univention Management Console) wasn’t “secure”, due to mixed content being loaded from demo.univention.com/ (see attachment "
UMC_HTTP_demo_background_01.PNG").
Downloading a file at all is alright-ish (although I would like to know why such a very often used file is not put locally, tracking-bitmap kind of thought?), but making the HTTPS fail due to that is troublesome.
Thanks for your feedback. Indeed this seems to break the security context of a https website. There is nothing against it to always load that content via a secure connection so I opened an issue to fix it in a future erratum.
You can easily change that specific line by replacing the http → https.
…or use sed to do this for you:
root@ucs:/usr/share/univention-management-console-frontend/js/dijit/themes/umc# mv umc.css umc.css.orig; sed 's|url("http://|url("https://|g' <umc.css.orig >umc.css