Hi,
I‘ve maintained my firewall with some more restriktive rules and found out, that the UCS is permanently calling the Root-DNS Server with UDP Calls on Port 53.
Is there any reason for this?
Usually the UCS should use the Standard Gateway for DNS requests.
Kind regards,
Frank
I just came across the same issue during the last security audit.
We’ve tightened our internal policies, and now only DoT traffic is allowed through the firewall. We’ve also disabled DNS access from the internal network to the internet. It’s not necessary, after all.
And I observed exactly the same behavior in the firewall log, continuous requests to DNS root servers. Can this behavior be changed? Is there a specific reason why the root servers are being queried constantly?
Because to me, this looks like a data protection issue for those where DoT is relevant.
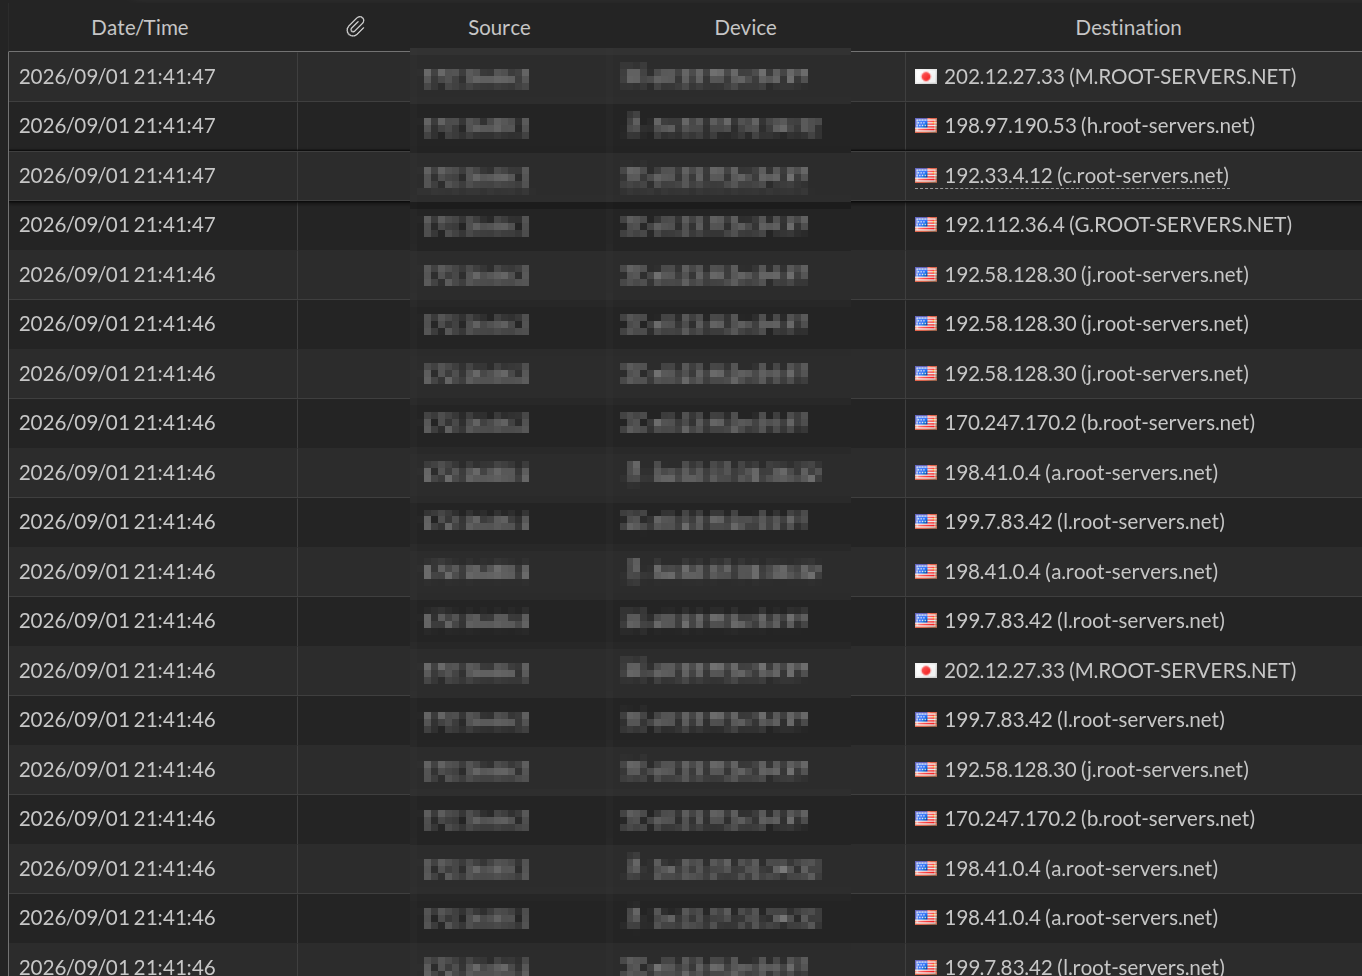
Thank you very much 
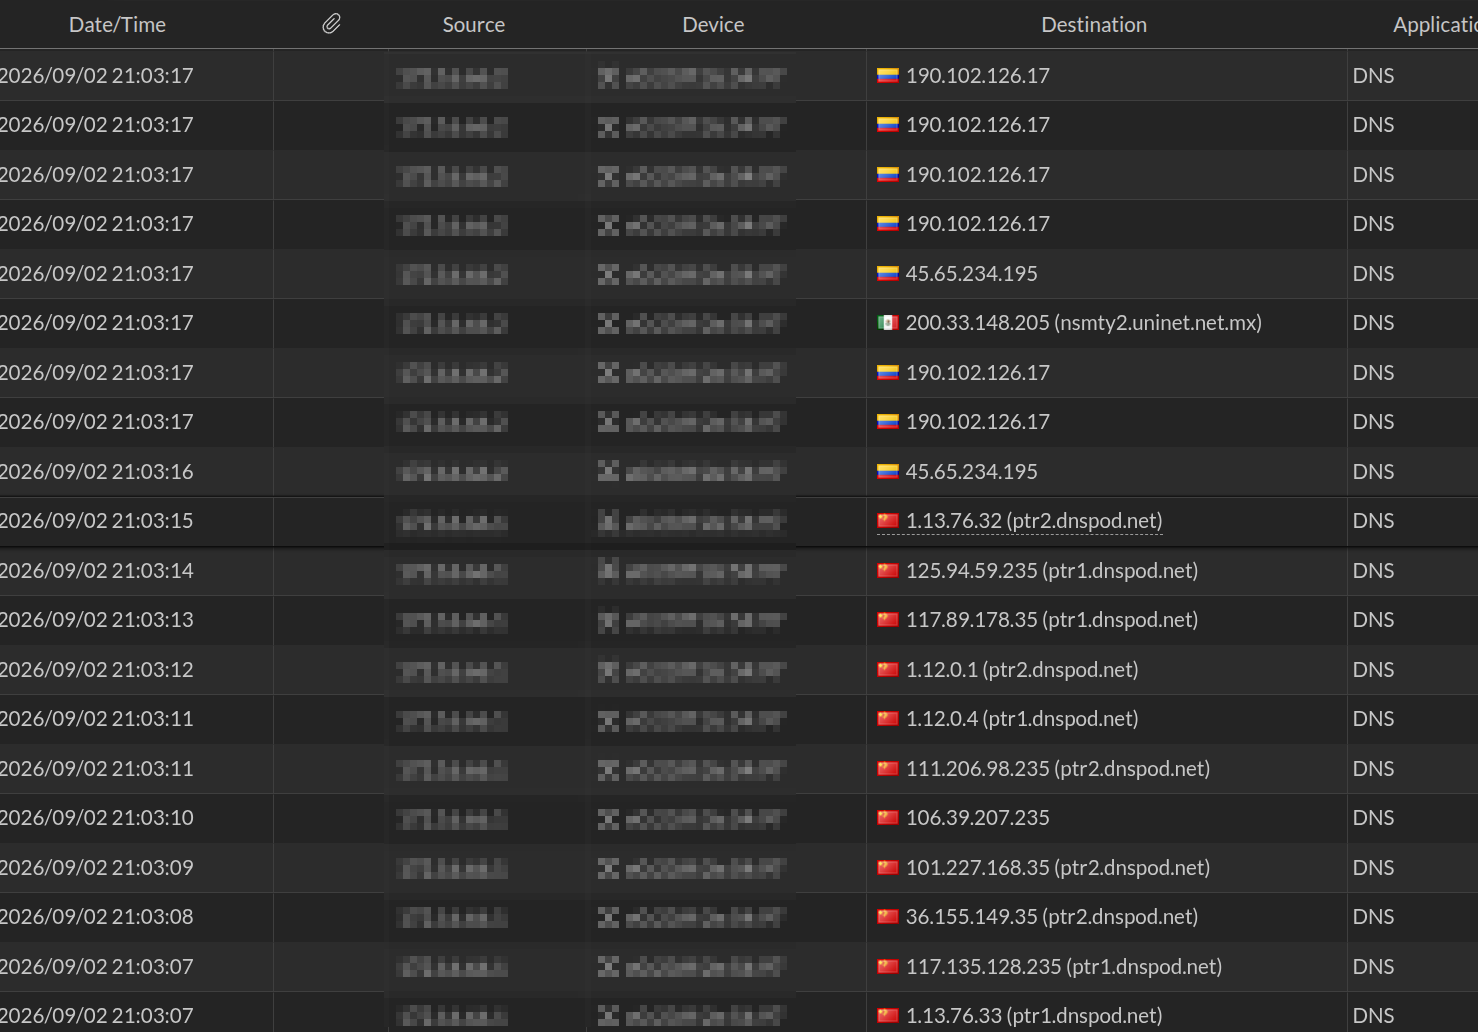
Yep, same here.
The jumping point is, the . zone is not set to forward only, even though you set a resolver.
Our central dns is not the UCS, but it is the autoritative server for the internal domain. Therefore, there is no need for the UCS to ask the roots.
In case your DNS backend is samba4 (ucr get dns/backend), you may change the template of samba’s named config:
python3 - <<'EOF'
p = '/etc/univention/templates/files/etc/bind/named.conf.samba4'
s = open(p).read()
old = "    print('\\ttype forward;')\n"
new = old + "    print('\\tforward only;')\n"
assert s.count(old) == 1, "String not found or not unique - nothing changed"
assert "forward only" not in s, "forward only is already in place"
open(p, 'w').write(s.replace(old, new))
print("OK, line added")
EOF
Commit, check and restart:
ucr commit /etc/bind/named.conf.samba4
grep -A6 'zone "."' /etc/bind/named.conf.samba4
named-checkconf
systemctl restart bind9
systemctl status bind9 --no-pager
Done! The UCS stopped to chat in my environment, immediately.
(Credits to my LLM with the least suspicion)
Thanks for your work; I’ll give this a try in my test environment. 
What I noticed when I block the RootDNS queries in UCS, then every “apt update” to Debian/Ubuntu takes longer. Timeout of approx. 5 seconds. Otherwise I didn’t notice any disadvantages. Even strange why only Apt has a delay.