Problem:
Duplicate key uid
Unerwarteter Fehler während der Bearbeitung der Anfrage an den Identity Provider
Unexpected error while processing the request to the identity provider
univention-app logs keycloak shows
2026-08-07 08:50:48,965 WARN [org.keycloak.services] (executor-thread-33) KC-SERVICES0013: Failed authentication: java.lang.IllegalStateException: Duplicate key uid (attempted merging values org.keycloak.userprofile.AttributeMetadata@1c450 and org.keycloak.userprofile.AttributeMetadata@1c450)
at java.base/java.util.stream.Collectors.duplicateKeyException(Collectors.java:135)
[…]
2026-08-07 08:50:48,982 WARN [org.keycloak.events] (executor-thread-33) type=“LOGIN_ERROR”, realmId=“ucs”, realmName=“ucs”, clientId=“https://portal.schein.ig/nextcloud/apps/user_saml/saml/metadata”, userId=“null”, ipAddress=“80.X.X.X”, error=“invalid_user_credentials”, auth_method=“saml”, redirect_uri=“https://portal.schein.ig/nextcloud/apps/user_saml/saml/acs”, code_id=“idDMUdfghtzunk2JUvm”, username=“sun_sp”
Investigation:
It looks like Keycloak is receiving two metadata entries with the same attribute name, “uid,” when building the user profile.
In Keycloak, AttributeMetadata is explicitly part of the user profile system; metadata such as read/write permissions, validators, etc., is managed there for each attribute name.
LDAP/User Federation would be the first suspect here. Keycloak allows federation providers such as LDAP to supplement or decorate user profile metadata. In the current Keycloak APIs, this exact integration between org.keycloak.storage.ldap and UserProfileMetadata is available.
Solution:
And in the user federation mappers there were exactly two identical uid mappers and also two username mappers.
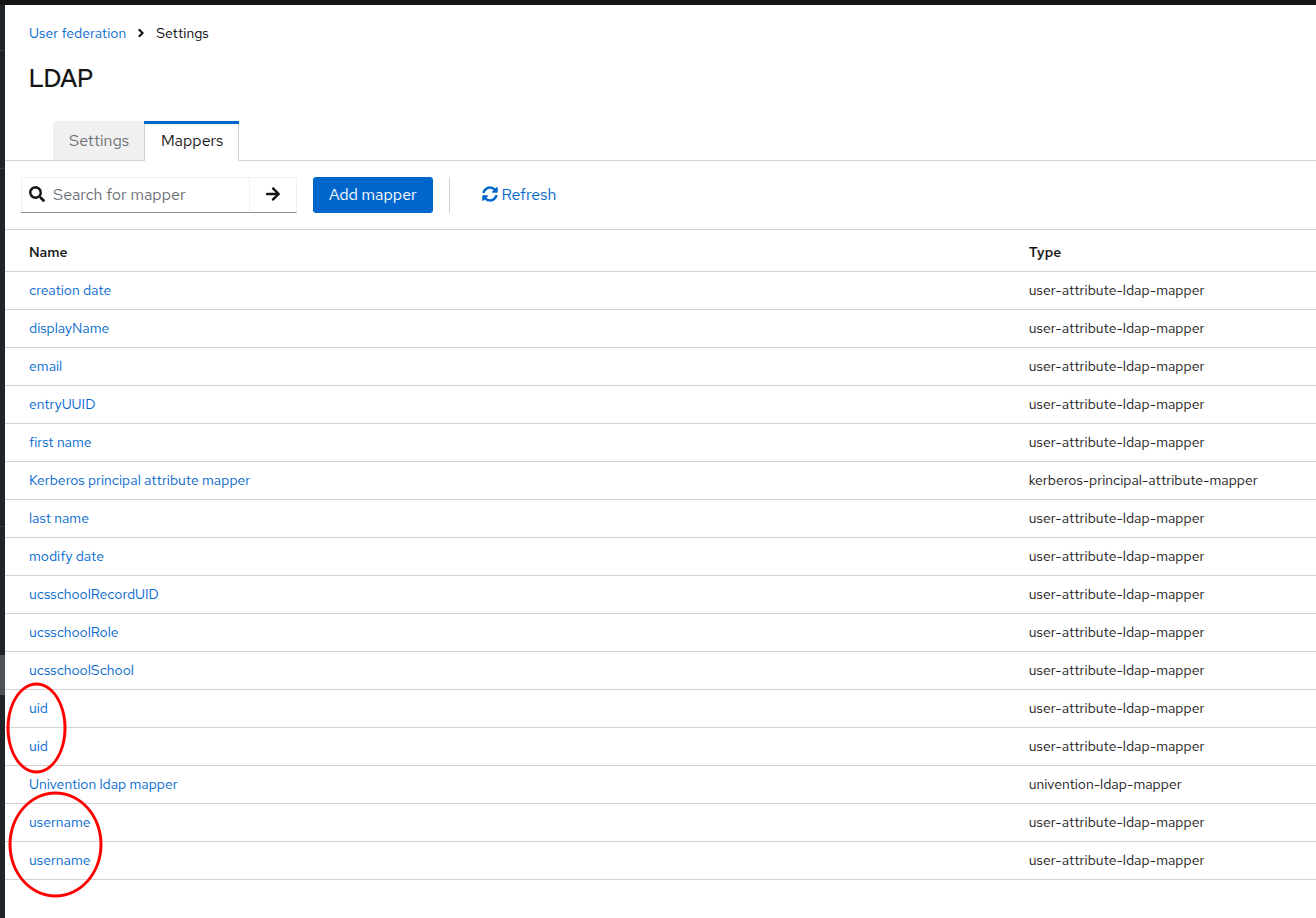
Removing one each solved the issue.
How can this happen.
- The UI does not validate duplocate entries, so maybe because of default the limited page view of 10 entries, these entries were not visible and added again.
- Or during import of some configurations, this could also be possible.